
How Do I Assess Our Essential Eight Maturity?
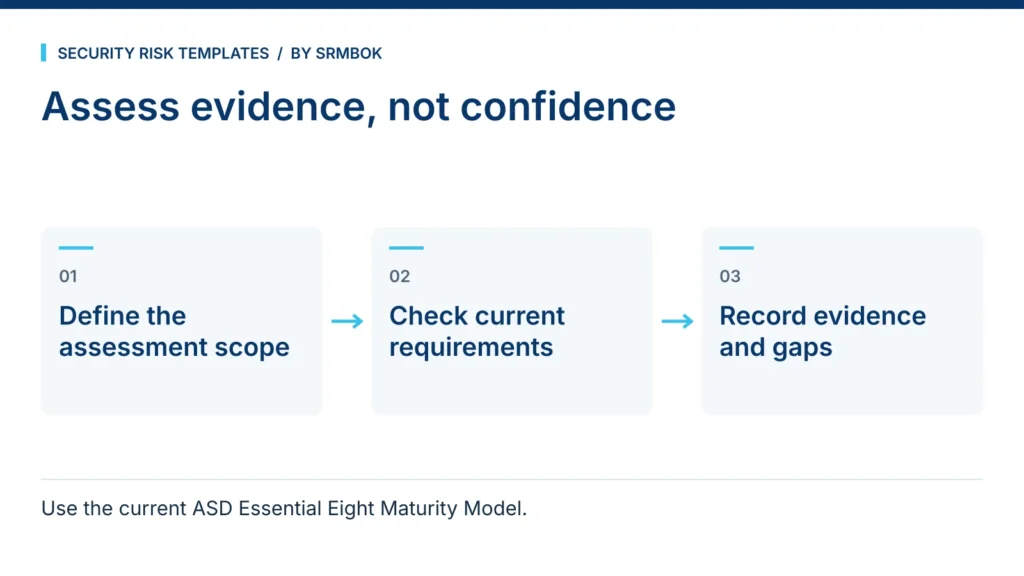
Assess Essential Eight maturity using current ASD requirements, scoped evidence and documented gaps. Use a practical tool as a starting point for the assessment.
How Do I Check Whether Information Is Safe to Paste into AI?
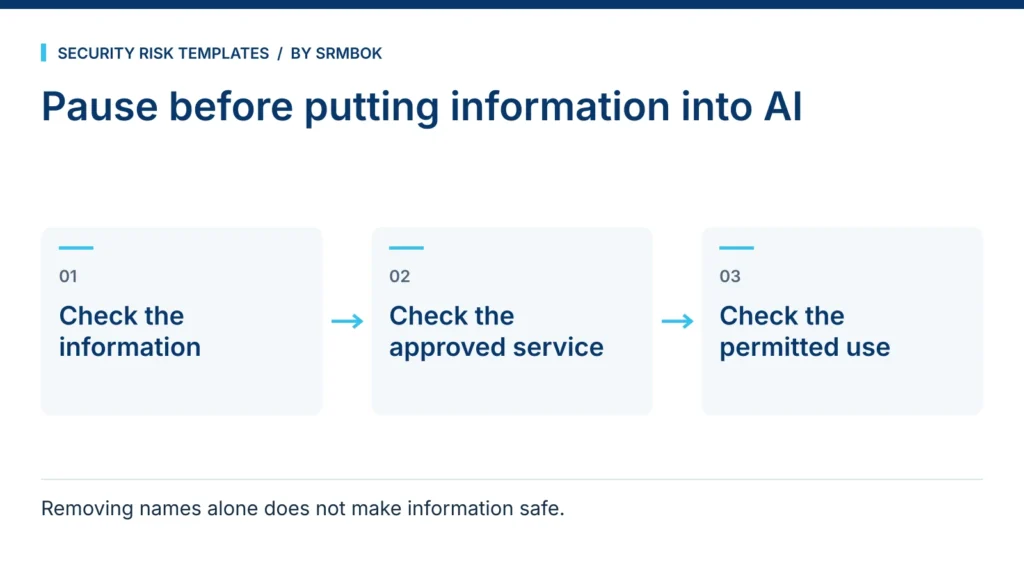
Check the information, approved AI service and sharing conditions before pasting. Spot sensitive details and understand why removing names may not be enough.
How Do I Make Cybersecurity Reminders Useful to Staff?
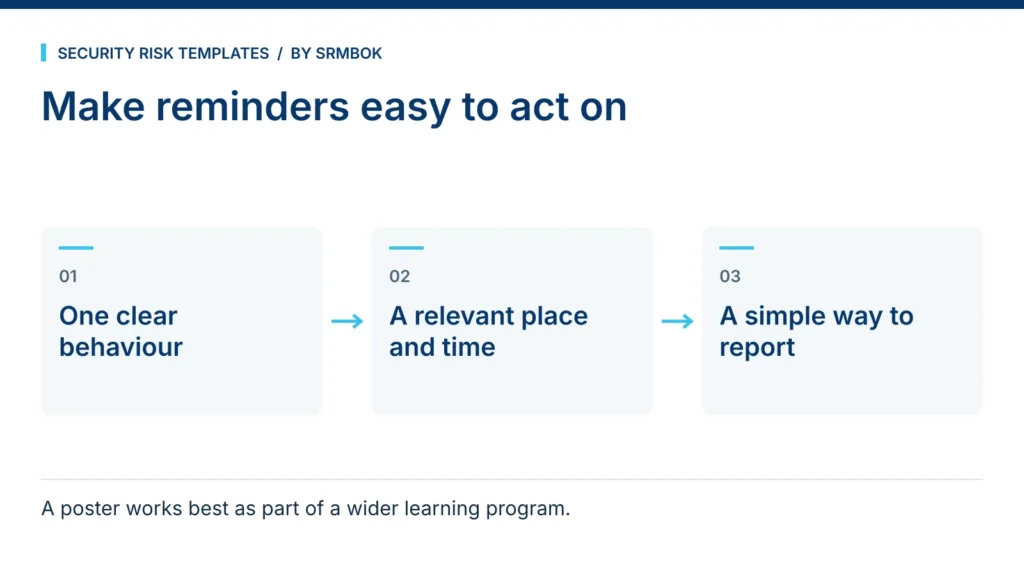
Free cybersecurity awareness posters staff will actually read, plus the placement, rotation and reinforcement habits that stop them fading into wallpaper.
Do We Need OSCAL for Our Security Compliance Work?
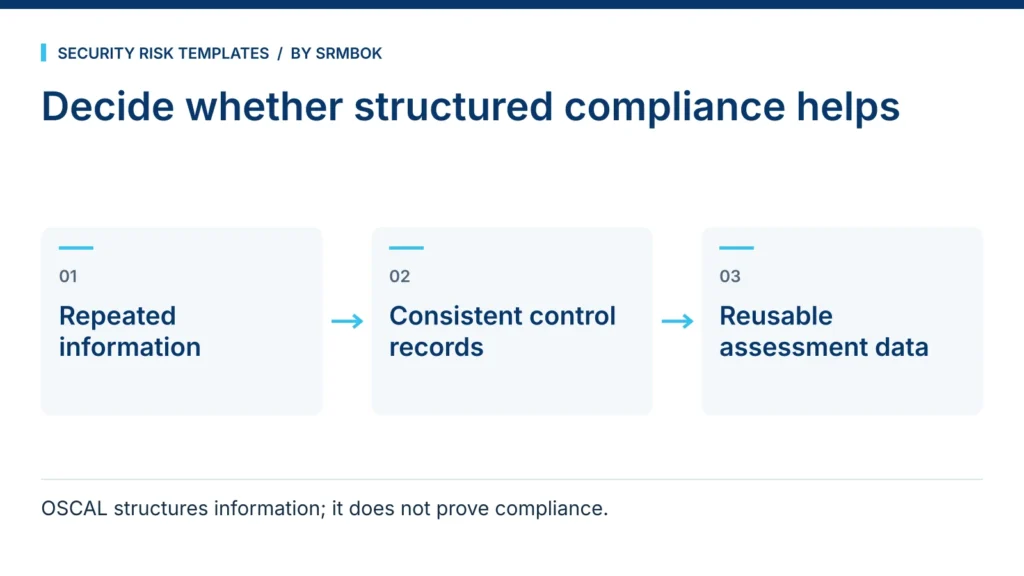
What is OSCAL? A plain-English explanation of the NIST control documentation standard and how to decide if your organisation needs it yet.
How Can I Use AI to Help Draft Security Risk Work?
Thirty ChatGPT prompts for risk practitioners, plus clear rules for what to paste into a prompt and what to always keep out.
How Do I Help Staff Recognise a Targeted Phishing Email?
Spearphishing vs phishing: the practical differences staff need to recognise, since the generic red flags in most training don’t catch a targeted attack.
What Cybersecurity Questions Should I Ask at a Board Meeting?
Five cybersecurity questions for boards to ask management, moving past ‘are we secure’ to ones with evidence-based answers behind them.
Which Essential Eight Maturity Level Should We Aim For?
An essential eight maturity level comparison for level 1 vs 2 vs 3, so you can pick a realistic target instead of guessing at compliance language.
How Do I Remove Sensitive Details from an AI Prompt Without Losing Its Meaning?
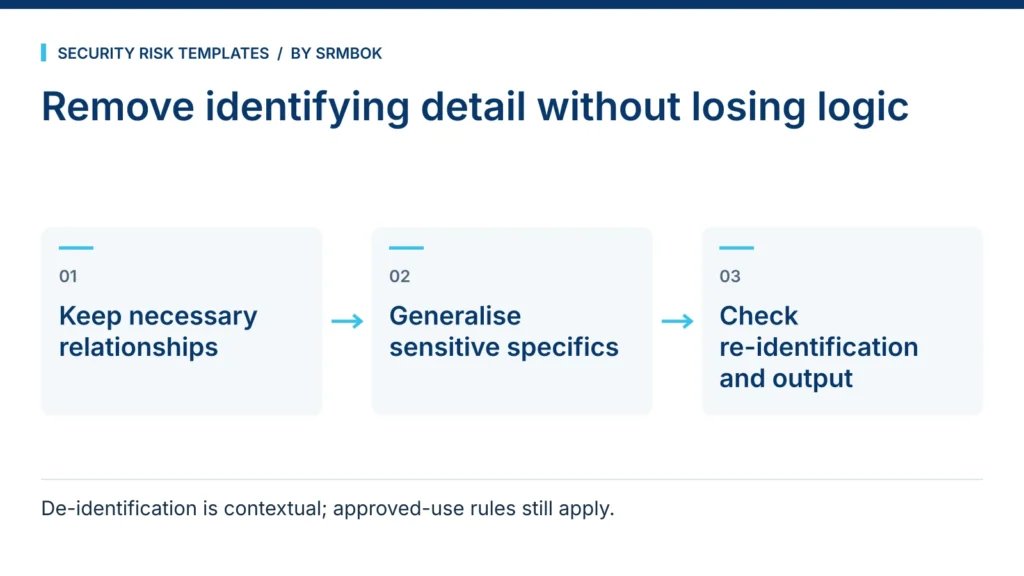
Remove or generalise identifying details in an AI prompt while retaining useful structure. Check re-identification risk, service approval and the resulting output.