Where do you start when you are given security risk responsibility? Start by agreeing what you are responsible for, finding urgent issues and recording a small number of decisions someone can act on. Starting security risk management does not require a complete new system in the first week.
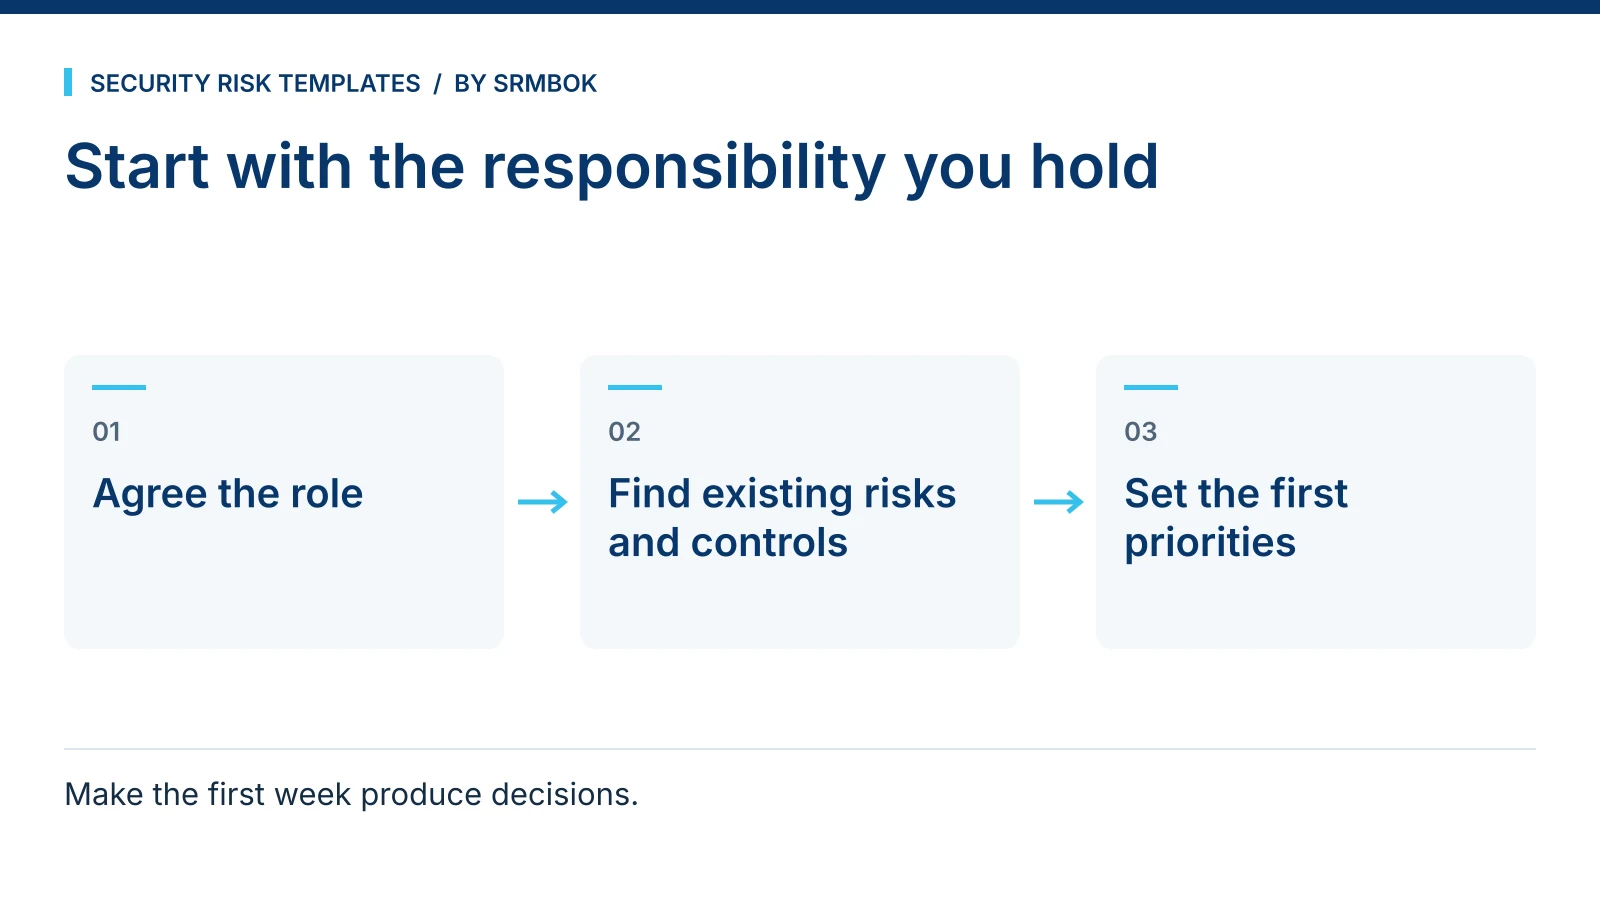
A first-week sequence
Use this as a practical starting sequence, not a promise to finish an assessment in five days. Urgent issues do not wait for their day in the list.
- Monday — establish remit and authority. Agree the first decision, scope, information access and approval roles.
- Tuesday — identify urgent exposures and obligations. Refer immediate issues through existing operational procedures and identify who confirms applicable requirements.
- Wednesday — find the existing record. Locate registers, assessments, incident records and controls; check their owners and currency.
- Thursday — meet the people doing the work. Test assumptions with site, service and control owners. Record missing evidence.
- Friday — agree the first working record and priorities. Record draft scenarios, immediate actions, proposed owners and assessment priorities. Set the next decision and review dates.
Do not fill evidence gaps with confident-looking ratings. Agree more time, specialist support or a narrower scope where the work requires it.
First, agree what the role actually covers
Ask the manager who assigned the work to confirm the sites, services and activities in scope. Clarify your authority to request information, commission assessments and recommend spending. Identify who can accept a risk and who can approve a treatment. These may be different people.
Write down the first decision the organisation needs. “Improve security” is too broad. “Decide how to control after-hours access at the main depot” gives you a starting point. If the remit remains unclear, use the questions in setting the scope of a security risk assessment.
Find out what already exists
Before creating another spreadsheet, locate the existing risk register, security policy, incident records, site plans, emergency arrangements and contracts that affect security. Ask the people doing the work which documents they actually use.
Keep a short discovery list:
| What to find | Why it matters | What to record |
|---|---|---|
| Existing assessments | Avoid repeating work or missing known issues | Owner, date, scope and review status |
| Recent incidents and near misses | Understand specific failure scenarios | What happened, controls involved and outstanding actions |
| Current controls | Separate plans from working arrangements | Who operates the control and how performance is checked |
| Decision authorities | Make recommendations actionable | Who accepts risk, approves money and owns delivery |
| Obligations and commitments | Identify work that needs specialist interpretation | Relevant requirement and person responsible for confirming it |
Do not assume a document is current because it is the first search result on the shared drive. Confirm its owner and status before treating it as the baseline.
Separate immediate action from the assessment backlog
A broken access door needs an operational response; it should not wait for the new risk register to be finished. Follow existing incident and emergency procedures for urgent issues, and involve the relevant owner. Record what was done and what still needs a decision.
Keep two things distinguishable in the same record: the urgent operational fix, with its action owner and completion evidence; and the underlying scenario that still needs formal assessment. An observation is not yet an assessed risk, and closing a maintenance ticket does not prove that the wider risk is acceptable.
For the remaining issues, distinguish an observation from a risk scenario. “Visitors are not signing in” describes an observation. “An unverified visitor could access the dispatch area and remove customer goods” describes one possible scenario to examine. Check whether that scenario fits the actual site before rating it.
Worked example: a facilities manager’s first week
In this fictional example, a facilities manager takes on security coordination for three depots. They cannot assess every site in five days. The operations director agrees that the first decision concerns after-hours access at the busiest depot.
The manager finds an old register, speaks with dispatch staff and reviews the access process with the site supervisor. A shared access code is still active after several contractors have left. The manager refers that issue for prompt action under the existing access procedure and records the response. The wider assessment covers who needs access, who approves it, how access is withdrawn and how exceptions are checked.
The week ends with an agreed scope, an owner for the immediate action, a list of missing evidence and a date for the assessment decision. It does not end with an unsupported claim that all three depots are secure.
Keep one working record
Use an existing approved register if it meets the need. If there is no usable register, start with a simple structure and a named owner. Avoid maintaining a private copy that nobody else can find or update.
Once the initial scope is agreed, follow the guide to building your first risk register. Keep treatment owners, dates and completion evidence with the relevant risk, using your organisation’s approved tracking process.
Free working resource
Start one useful working record
The Risk Register Starter Pack gives you a simple register, treatment plan and summary supplied as an editable Word document and a PDF. Adapt it to your remit and existing process, and label preliminary observations and evidence gaps clearly.
Download the free Word and PDF Starter Pack
Opens the SRMBOK product page. Add the free item to your cart and complete the $0 order to receive the download. Check the newsletter choice at checkout.